ISO 27001, Without the Overwhelm
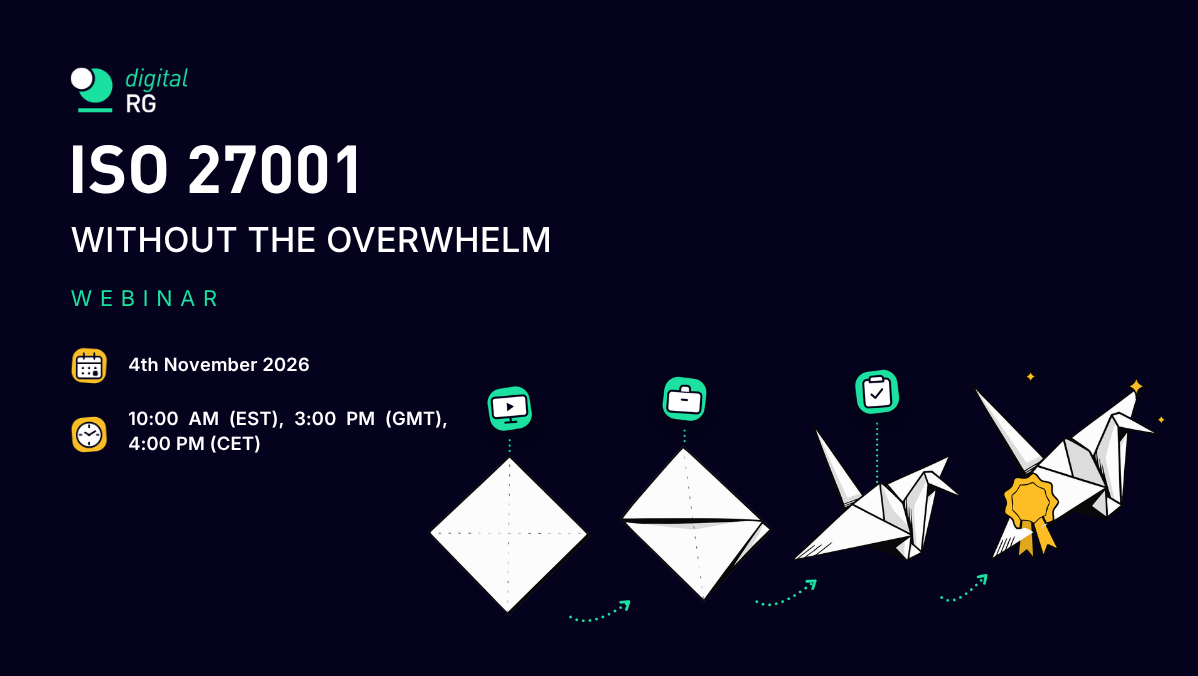
ISO 27001, Without the Overwhelm
ISO 27001 has a reputation for being heavy going: a long list of controls, policies to write from scratch, and an auditor who wants evidence for all of it. But it does not need to be that way.
In this session, we’ll be joined by people who have taken their organisations through ISO 27001 certification. They’ll share how they broke the process down into manageable steps, what worked for them and what they learnt along the way.
Participants will come away with practical guidance in three key areas:
Where to start
How to scope your information security management system, carry out a gap analysis and prioritise what matters most, so you are not trying to do everything at once.
- What good evidence looks like
The policies, records and risk assessments auditors expect to see, and how to build them into the way your teams already work. - How to prepare for your audit
What to expect at each stage of certification, where organisations commonly fall short, and the lessons our speakers would pass on to anyone starting the process.
The session is designed to make ISO 27001 feel more practical and manageable, with first-hand insights from organisations that have already been through the certification journey.
➔ Register here.
Featured eLearning Module

Conceitos de Probabilidade e Estrutura de Prêmios em Loterias, Cassinos e Apostas Esportivas
Upcoming Events
May 18, 2027 - May 21, 2027
13th EL Congress 2027
February 23, 2027 - February 25, 2027
EL Seminar - Combatting Illegal Gambling

January 20, 2027 - January 22, 2027
EL/WLA Marketing Seminar 2027
December 15, 2026 - December 15, 2026
When It Matters Most: Lotteries Supporting Nature and Communities